Devlore: Device Interrupt Protection for Confidential VMs
International Symposium on Research in Attacks, Intrusions and Defenses (RAID 2026)
Abstract
Modern confidential computing executes sensitive computation in an abstraction called confidential VMs and protects it from the hypervisor, host OS, and other co-resident VMs. It has been shown that an attacker can inject malicious interrupts to break the confidentiality and integrity of confidential VMs.
We present Devlore, a device interrupt isolation mechanism that protects confidential VMs from interrupt manipulation attacks. Our design employs a delegate-but-check strategy by offloading interrupt management to the hypervisor while adding correctness checks in trusted software.
We prototype our design on the Arm Confidential Computing Architecture (CCA). We evaluate it on Arm FVP using four diverse devices attached to confidential VMs and report costs on a Rock 5B board. Our case studies demonstrate the feasibility of real-world use cases, while Devlore incurs only 0.06% overhead for typical integrated GPU applications.
Authors
ETH Zurich
Showcase
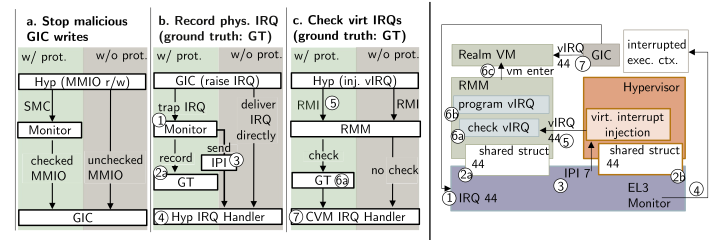
Delegate but check in three steps — protect the interrupt controller, record new interrupts, and check virtual interrupts..
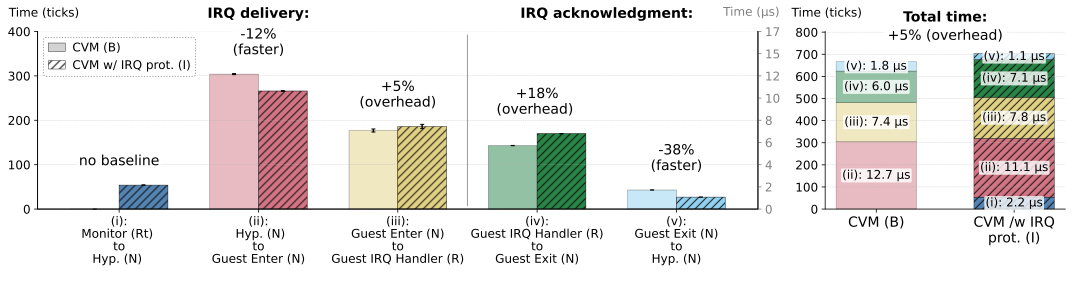
Breakdown of Interrupt cost. Check paper for details.
Case study on Fixed Virtual Platform (FVP). Booting a CVM with interrupt protection.
Case study on Fixed Virtual Platform (FVP). Booting a CVM without interrupt protection.
Cite Us
@inproceedings{bertschi2026devlore,
  title     = {Devlore: Device Interrupt Protection for Confidential VMs},
  author    = {Bertschi, Andrin and Sridhara, Supraja and Kuhne, Mark and Schl{\"u}ter, Benedict and Groschupp, Friederike and Thorens, Cl{\'e}ment and Dutly, Nicolas and Capkun, Srdjan and Shinde, Shweta},
  booktitle = {International Symposium on Research in Attacks, Intrusions and Defenses (RAID'26)},
  year      = {2026}
}